Is your Odoo an open door?
Check your Odoo security in two minutes with our free healthcheck module
Why Odoo is a target
Your ERP holds your customers, invoices, contracts and payroll. Automated scanners and bug bounty hunters probe Odoo login, password-reset and database pages every day. Attackers don’t need a zero-day: risky defaults are usually enough.
These are the six weaknesses we find most often in Odoo environments:
1: Open database manager
/web/database/manager is reachable from the internet, often protected only by a weak or default master password. Anyone who gets in can back up, restore, or drop your entire database. This is the first thing attackers check.
2: Administrators without 2FA
An Odoo administrator can install modules and run code on your server. When two-factor authentication isn’t enforced, one phished or reused password is enough to take over the whole instance.
3: Demo data in production
Databases created with demo data keep demo users whose passwords are publicly known. It’s a ready-made login for anyone who knows Odoo.
4: Free sign-up by default
Installing the sign-up module lets anyone on the internet create a portal account. That widens the authenticated attack surface for access-rights and portal abuse.
5: Hidden custom code
Python code in server actions and scheduled actions is a classic persistence technique. It runs with high privileges and is rarely reviewed after go-live.
6: No visibility
There’s no WAF in front of Odoo and no logs in a SIEM, so brute-force attempts, reconnaissance and abuse go unnoticed until something breaks. You can’t respond to what you can’t see.
Our free Security Healthcheck checks all of this, and 24 more settings, inside your own Odoo. Know where you stand before an attacker does!
Shift Left Security provides your company security software and services!
Cyber attacks are becoming more sophisticated every year, while regulations such as NIS2, DORA and GDPR raise the bar for every organisation. Most IT teams simply don’t have the time or specialist skills to keep up.
Outsourcing security to a specialised partner gives you senior expertise and 24/7 coverage without building it in-house. That’s why growing companies rely on Shift Left Security.
1.
Security Testing and Assessments
We find your vulnerabilities before attackers do. We offer penetration tests of infrastructure, websites, web applications and APIs, plus vulnerability assessments and configuration audits. Each one ends in a clear report with prioritised, practical recommendations.
3.
Continuous Scanning Security Services
Security is not a one-time check. We continuously monitor your external attack surface, websites and endpoints, detect threats as they emerge, and support you with incident response and security operations.
2.
Security Training and Awareness
Your employees are your first line of defence. We train them in security best practices and how to recognise phishing and social engineering, so security becomes part of everyday work.
4.
Security Consulting and Advisory
We help you build and implement a security strategy that fits your business. That includes risk assessments, ISO 27001 and NIS2 compliance guidance, security architecture reviews and tailored solutions.
+32 2 897 34 34
From identifying vulnerabilities and educating your people to continuous monitoring and strategic advice, Shift Left Security covers every layer of your cybersecurity. Your Innovative Cybersecurity Ally: Securing Tomorrow, Starting Today.
Free Security Healthcheck module for Odoo
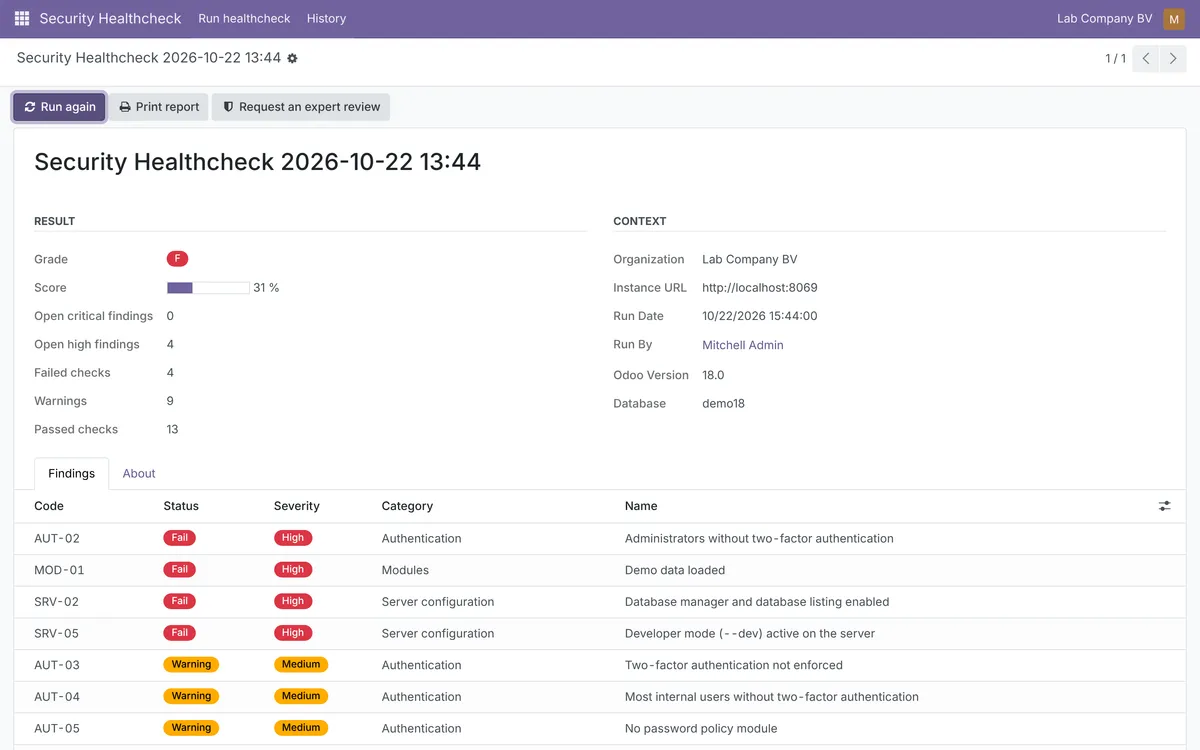
Install the module from the Odoo Apps store and click Run healthcheck. Within seconds you get a score, a grade from A to F, and a clear recommendation for every finding: server configuration, authentication and 2FA, admin accounts, API keys, custom code, modules, mail and web. That’s 30 checks in total.
t is read-only: nothing is changed, no passwords are tested and no data leaves your server. You can print a PDF report for your integrator, hosting partner or management. It supports Odoo 17 and 18, on Odoo.sh and self-hosted.
1.
External exposure scan
We look at your Odoo the way an attacker sees it from the internet: exposed endpoints, the database manager, XML-RPC/JSON-RPC, version disclosure, TLS configuration and WAF coverage. A healthcheck inside Odoo can’t see any of this.
3.
Web application firewall
We put a managed WAF and DDoS protection in front of Odoo. It blocks brute-force attempts, scanners and known attack patterns before they reach your server, and is tuned so your users and integrations keep working.
2.
Odoo penetration test & code review
Our offensive security specialists test access rights, portal and API abuse, and multi-company separation. They also review your custom and third-party modules, where most real-world Odoo vulnerabilities live.
4.
24/7 monitoring
We collect your Odoo, server and WAF logs in a managed SIEM, backed by EDR on the Odoo server. Suspicious logins, new admin accounts and attacks are detected and escalated around the clock.
Is the Security Healthcheck really free?
Yes. It is published under the LGPL-3 licence on the Odoo Apps store, without registration or licence key.
Does the module send data to Shift Left Security?
No. All checks run inside your Odoo, read-only, and nothing leaves your server. The PDF report is only shared if you decide to send it.
Which Odoo versions and hosting types are supported?
Odoo 17.0 and 18.0 (19.0 coming), on Odoo.sh and on self-hosted or partner-hosted installations. Odoo Online (SaaS) does not allow third-party modules - for Odoo Online we offer the external exposure scan.
Can the healthcheck break anything?
No. It changes no settings and does not try passwords. You can uninstall it at any time without side effects.
We use an Odoo integrator. Do we still need you?
Integrators build and maintain your Odoo; we test and protect it like an attacker would. We work alongside your integrator and hosting partner.
+32 2 897 34 34
Integrators build and maintain your Odoo. We test and protect it the way an attacker would look at it, working alongside your integrator and hosting partner. Start with the free healthcheck, then let us cover what it can’t see.
Let's Connect!
From identifying vulnerabilities and educating your people to continuous monitoring and strategic advice, Shift Left Security covers every layer of your cybersecurity. Your Innovative Cybersecurity Ally: Securing Tomorrow, Starting Today.
+32 2 897 34 34
